
Rule-Based Automation vs AI: 6 Practical Criteria
The choice between rule-based automation vs AI isn’t about which technology is more advanced — it’s about which process you’re automating. Rule-based automation follows fixed, predictable logic: “if this, then that.” AI-driven automation comes into play when a process requires interpretation — of a text, a document, or a context that varies.
The short answer: use rule-based automation when the rules are stable and inputs are structured; consider AI when there’s ambiguity to interpret, always paired with human oversight, decision logging and periodic review. The two models can even coexist in the same workflow. Below are the criteria for deciding, case by case, without losing control or compliance.
Rule-based automation vs AI: telling them apart in practice
Rule-based automation is a set of programmed rules that execute the same action whenever the same conditions appear. One example: issuing an invoice automatically once an order is marked “paid” in the system. There’s no interpretation — just condition-checking and execution.
AI-driven automation, on the other hand, handles unstructured or ambiguous data: a customer email, a PDF contract, a scanned receipt. The AI needs to “understand” the content before acting, which introduces a layer of uncertainty that rule-based automation doesn’t have.
This distinction matters because it changes the type of risk involved. With rule-based automation, risk lies in poorly designed rules or unforeseen exceptions. With AI automation, risk also includes misinterpretation, model bias and, depending on the data involved, data protection requirements. It’s worth noting that personal data processing — collection, use, access, storage, deletion — can occur even in automations with no AI at all, according to Brazil’s National Data Protection Authority (ANPD, 2026). In other words, the presence of personal data, not the use of AI, is already a trigger for compliance safeguards.
6 criteria for choosing between the two models
Before picking a technology, map the process using these criteria. They help avoid the most common mistake: applying AI where simple rules would do, or forcing fixed rules onto a process that genuinely requires interpretation.
- Stability of the rules: if the process has followed the same logic for months with few changes, rule-based automation is enough. Example: approving reimbursements up to a fixed amount.
- Structure of the input data: spreadsheets, forms and standardized fields favor fixed rules. Free text, audio or images call for AI to extract or classify information.
- Predictability of exceptions: if exceptions are finite and known (e.g., “if the ID is invalid, send for manual review”), rules suffice. If exceptions are varied and unpredictable, AI can help triage, but shouldn’t decide alone.
- Risk and impact of the decision: Brazil’s Gov.br portal (2026) recommends evaluating AI automation by risk, benefit, legal requirements, efficiency, standardization, traceability and the need for human oversight. Low-impact decisions can tolerate more AI autonomy; critical decisions require a human in the loop.
- A clear process owner: without someone assigned to handle exceptions, audit results and adjust rules or models, any automation tends to degrade over time.
- Volume and expected return: investing in automation, with or without AI, only pays off when execution volume justifies the implementation and maintenance cost. Occasional processes rarely justify a dedicated project.
AI automation and data compliance risks
When a process involves personal data — names, ID numbers, purchase history, résumés — automation, with or without AI, falls under data protection law. The ANPD (2026) advises mapping and documenting processing operations, their purposes, legal bases, and the technical and administrative safeguards in place. This applies equally to rule-based automation that processes customer data and to an AI workflow that reads résumés.
One specific point for AI: decisions made exclusively through automated processing can give the data subject the right to request human review (ANPD/TSE, 2026). Organizations also need to be ready to explain the criteria and procedures used, respecting trade and industrial secrets where applicable. This means a résumé-screening process run entirely by AI, for instance, should have a human reviewer available for contested cases.
Another recommended document is a data inventory, identifying purposes, legal bases, data categories, data sharing, international transfers, and the existence of automated decisions (ANPD/TSE, 2026). For higher-risk processes — for example, those affecting access to credit, employment or benefits — a Data Protection Impact Assessment may be required, describing risks to civil liberties and the mitigation measures adopted (Brazilian Federal Government, 2026).
In practice, Kairen recommends treating this mapping as part of the automation project itself, not as an afterthought. That avoids rework and reduces the risk of building a workflow that later needs to be redone for compliance reasons. Anyone who has already decided to automate but is still unsure about the technical approach — API or RPA (robotic process automation) — can dig deeper into that choice in our API or RPA comparison.
When rule-based automation makes sense — and when it doesn’t
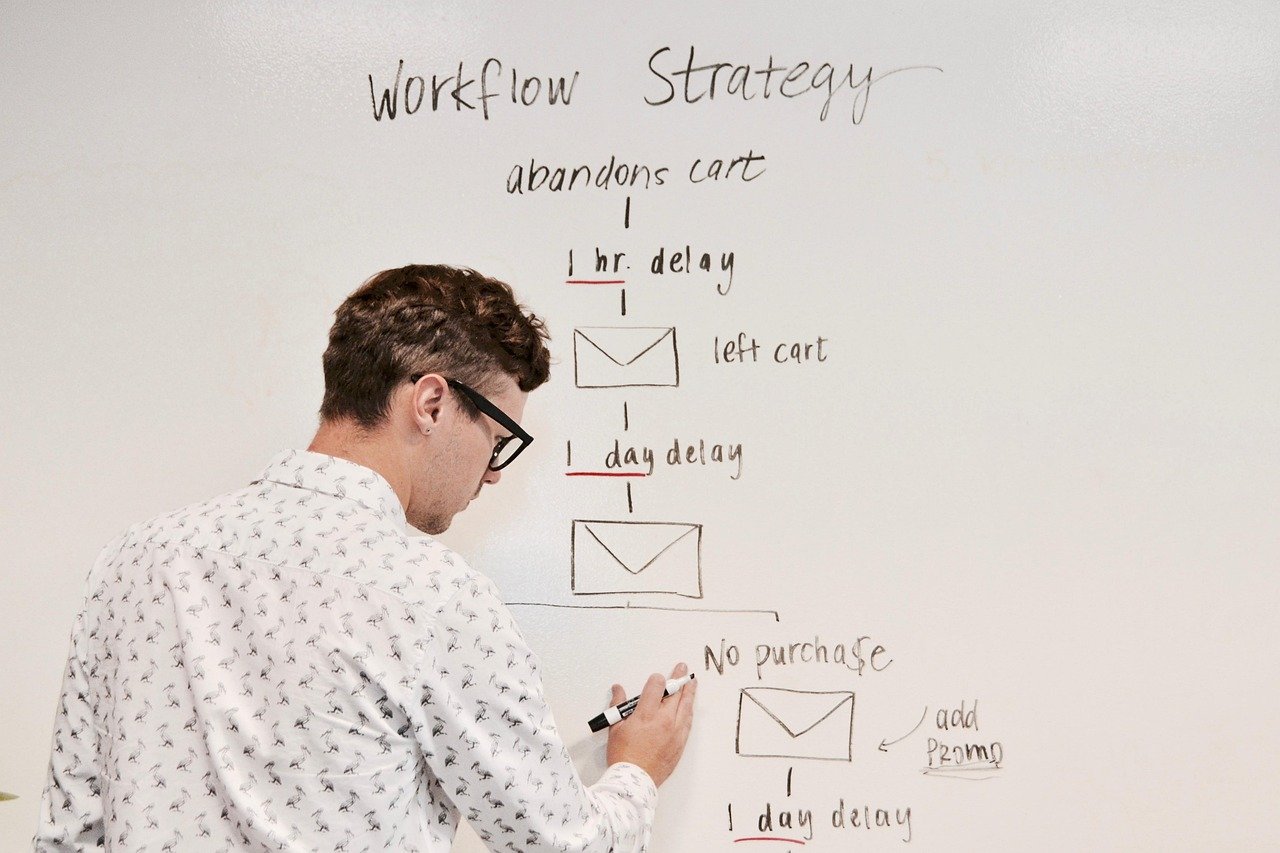
Rule-based automation makes sense when a process is repetitive, inputs are structured, and exceptions are predictable. A typical example: automatic bank reconciliation, where the system compares values and flags discrepancies for manual review. This also holds when there’s enough volume to justify the project, defined success metrics, and someone responsible for auditing and maintenance.
It doesn’t make sense to force fixed rules when a process changes frequently, has no defined owner, deals with inconsistent data, or involves critical decisions with no possibility of human review. In those cases, trying to automate without AI tends to produce a rigid system full of manual exceptions that cancel out any efficiency gains.
A practical scenario: a logistics operation that receives orders through a standardized form can fully automate label and invoice generation with fixed rules. But if orders arrive by email in varied formats, extracting that information likely requires AI to interpret the text before rule-based logic takes over — a hybrid workflow, which is more common than people assume.
AI automation: when it pays off and what limits to set
AI-driven automation pays off when a process requires interpreting natural language, classifying varied documents, or analyzing context that fixed rules simply can’t cover. Examples include triaging support emails, extracting data from contracts, or classifying tickets by urgency.
The risk emerges when AI is left to decide alone in high-impact situations, without human oversight or a record of the decisions made. NIST (the U.S. standards and technology institute), in material shared by Brazil’s Institutional Security Office (GSI, 2026), proposes organizing risk management around governance, mapping, measurement and continuous management throughout the system’s lifecycle. That means adopting AI isn’t a one-time event — it’s an ongoing monitoring process.
Companies already using AI connected to internal knowledge bases, or evaluating ready-made tools versus custom ones, should review our posts on AI connected to a knowledge base and AI governance for business, which go deeper into the controls needed before scaling this kind of automation.
How to decide in practice: an evaluation checklist
Before commissioning or building any automation, it’s worth running through a simple evaluation checklist for each process:
- List candidate processes and separate those with stable rules from those requiring interpretation.
- Check whether personal data is involved and, if so, identify the legal basis and the party responsible for processing it — keeping in mind that controller and processor play distinct roles under data protection law, as Brazil’s Ministry of Science, Technology and Innovation (MCTI, 2026) notes: the controller defines the purposes; the processor handles the data according to the controller’s instructions.
- Define who reviews exceptions and how often automation results are audited.
- Estimate volume and return before investing in either model.
This checklist doesn’t replace a legal review, but it helps objectively identify which processes are ready for automation and which still need adjustments first. Anyone starting this mapping exercise can benefit from our content on when it’s worth automating, which covers initial prioritization criteria.
Conclusion
The choice between rule-based automation vs AI comes down to the type of data, the stability of the rules, and the risk of the decision — not the newest technology available. Structured, predictable processes call for fixed rules; processes involving interpretation of text or context call for AI, always paired with human oversight and decision logging. One example of a project that combined systems development with process automation is the Carnier Web case, focused on systems development.
If your operation has manual processes that haven’t yet been mapped against these criteria, the next step is a technical conversation to identify where each model applies. Talk to Kairen’s automation team or visit our contact page to assess your case.
Frequently asked questions
Rule-based automation vs AI: which one is cheaper?
Generally, rule-based automation has a lower implementation cost, since it doesn’t require model training or tuning. But total cost depends on process volume and the ongoing maintenance of rules over time.
Can the two models be combined in the same process?
Yes. It’s common to use AI to interpret or classify unstructured input, then apply fixed rules to execute the action based on that classification. This hybrid model is frequent in document triage.
Does AI automation always require a Data Protection Impact Assessment?
Not always. The assessment is recommended when processing could create significant risks to civil liberties or the data subject’s fundamental rights, per guidance from Brazil’s Federal Government (2026). Low-risk processes may not require it, but data mapping is still necessary.
Who is legally responsible for data handled by an outsourced automation?
It depends on the contract. According to Brazil’s MCTI (2026), the controller defines the purposes of processing and the processor handles the data per the controller’s instructions — which is why it’s important to formalize this relationship before automating any process involving personal data.
Sources
- AI automation evaluation matrix — Gov.br Portal
- Frequently asked questions on data processing — ANPD
- LGPD Guide — ANPD/TSE
- LGPD Best Practices Guide — Brazilian Federal Government
- Guidance on personal data processing — ANPD
- AI Risk Management Framework — NIST, via GSI
- Best practices: controller and processor — MCTI